Secure your AI-built app before launch

No reviews yet, be the first!
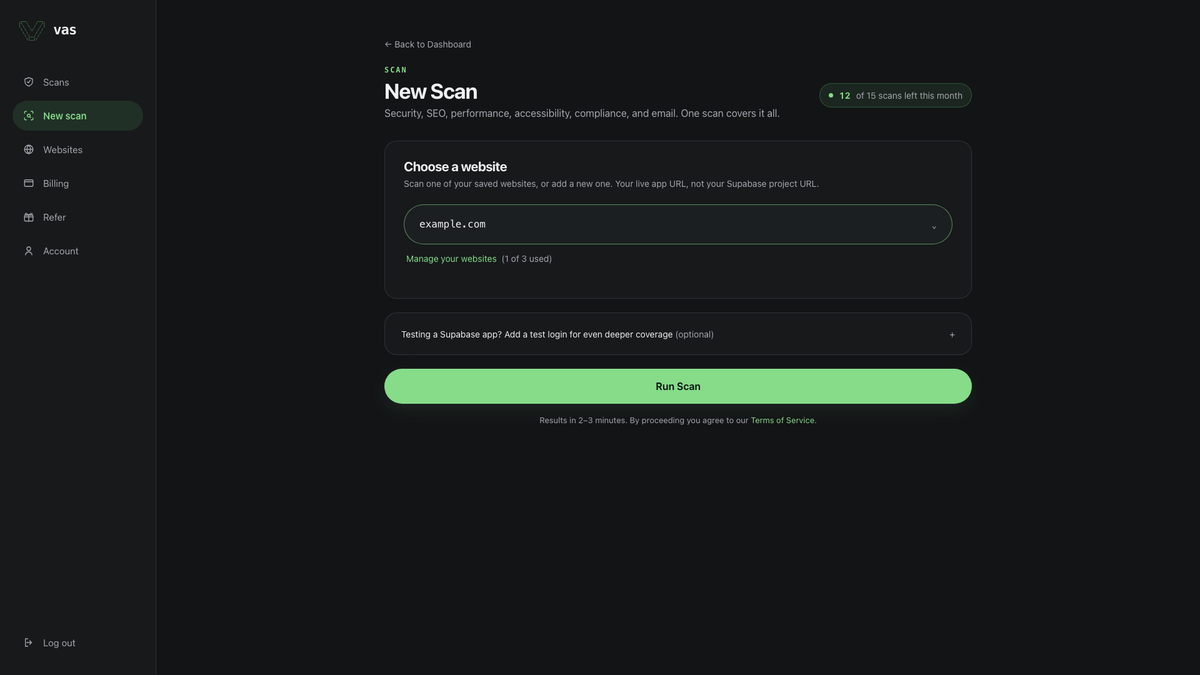
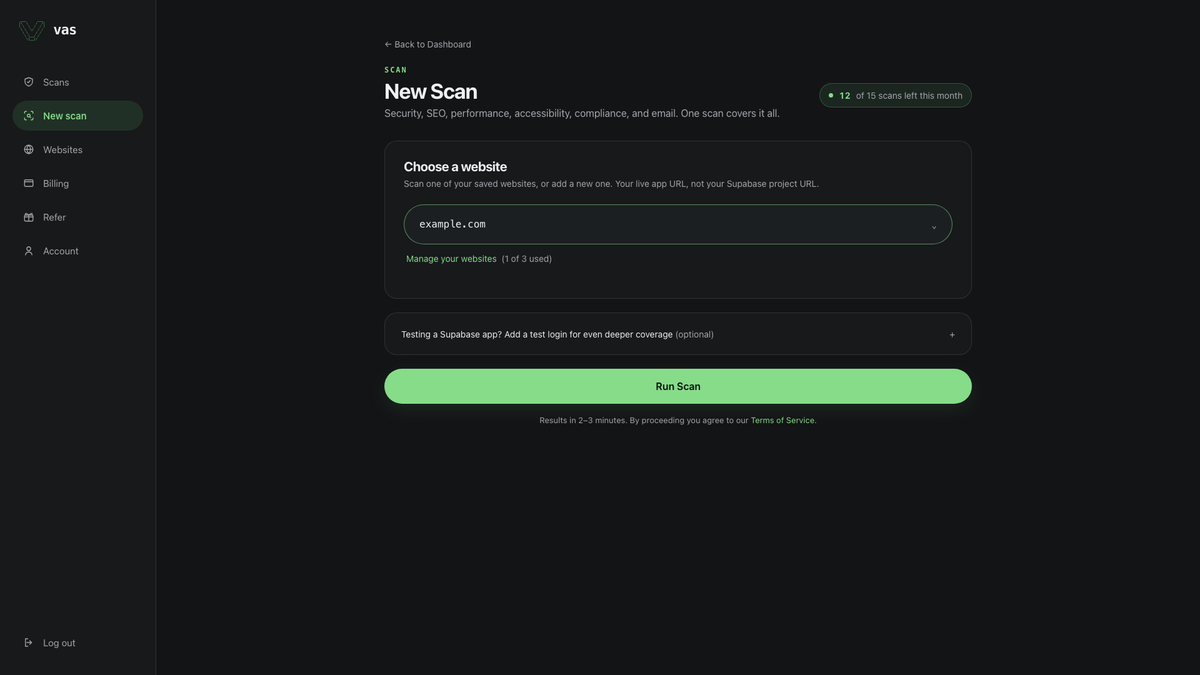
New scan
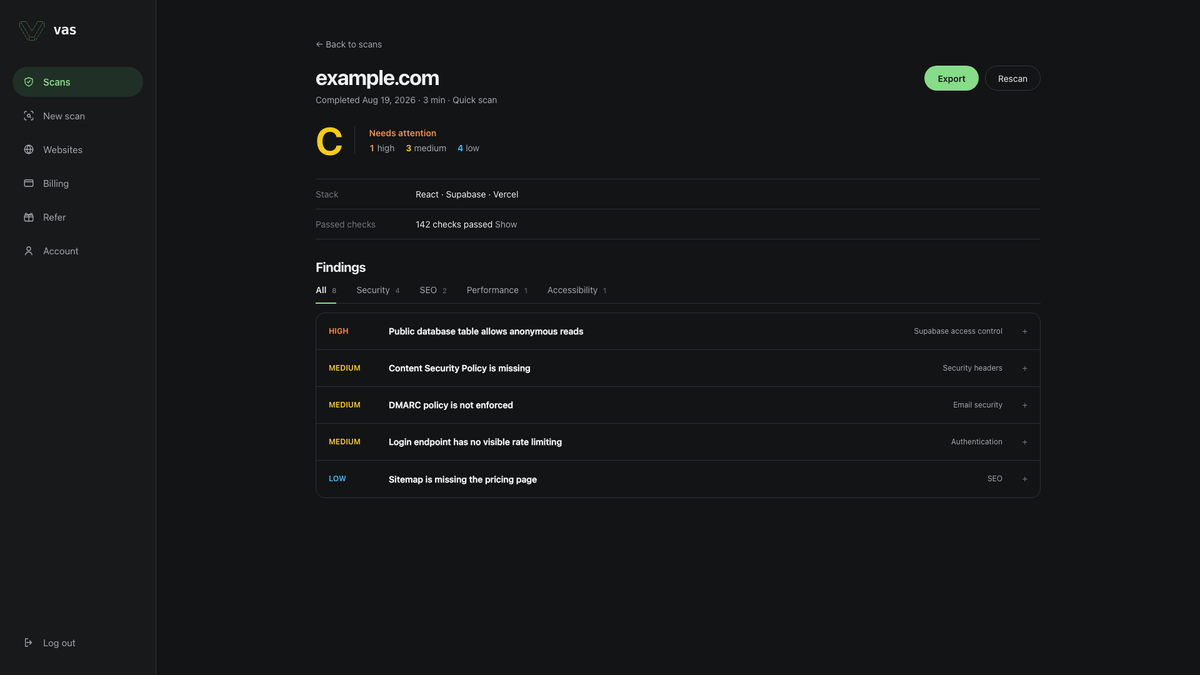
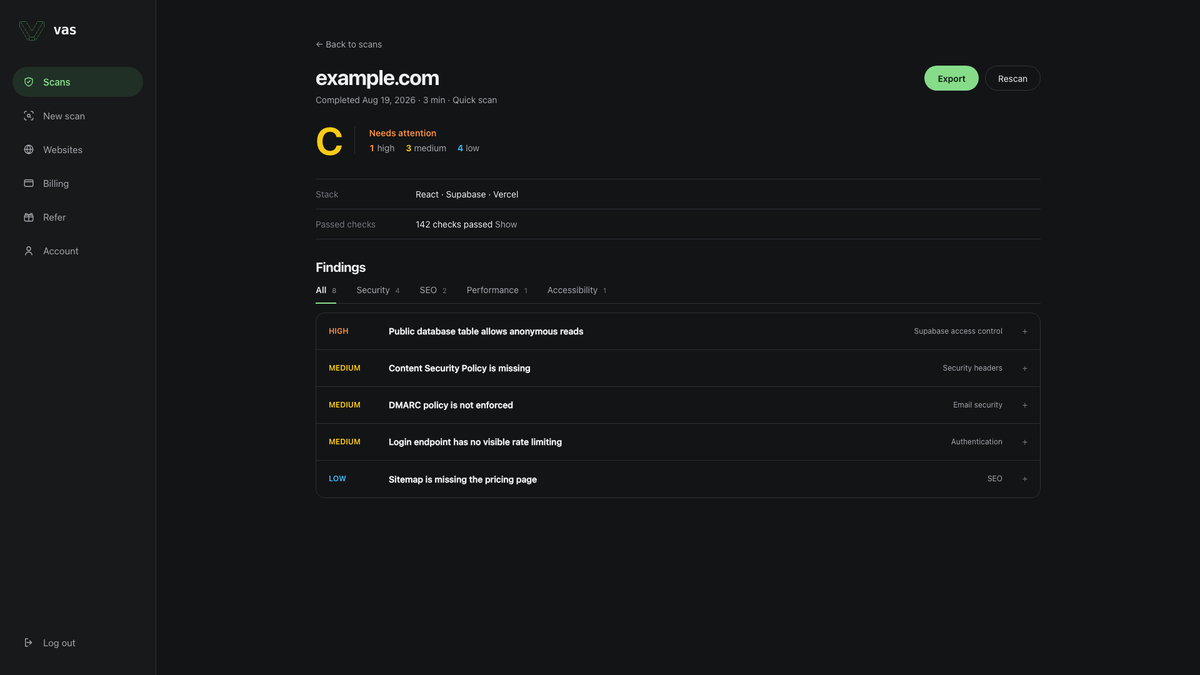
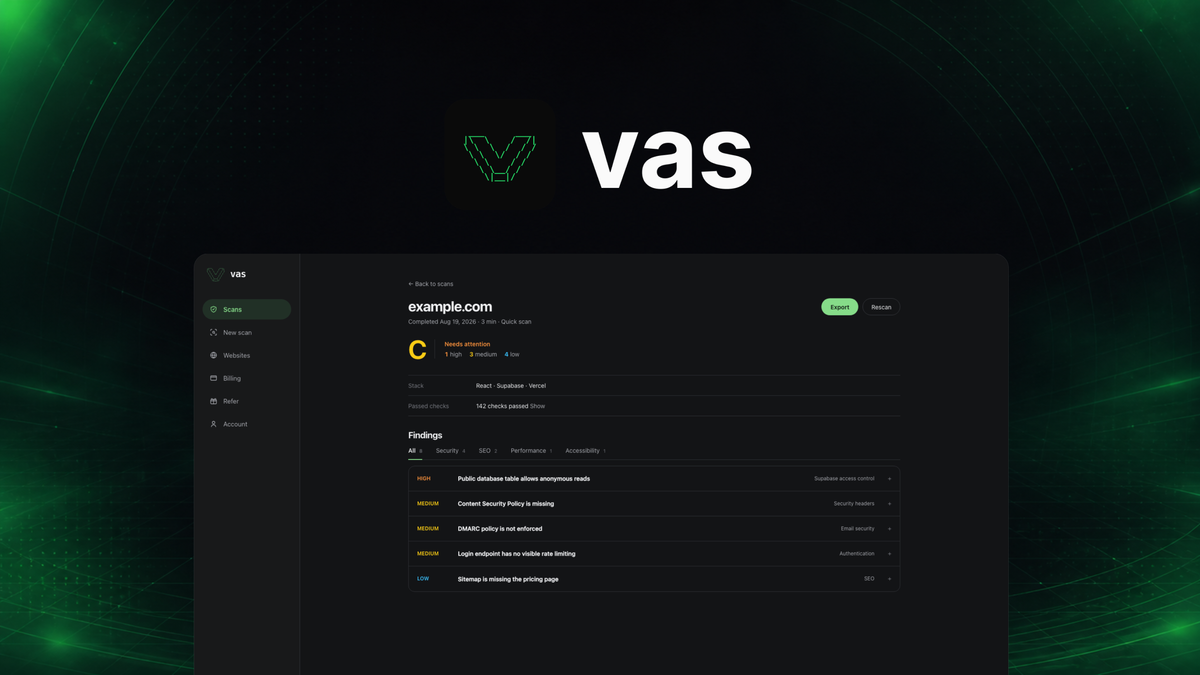
Scan results with severities
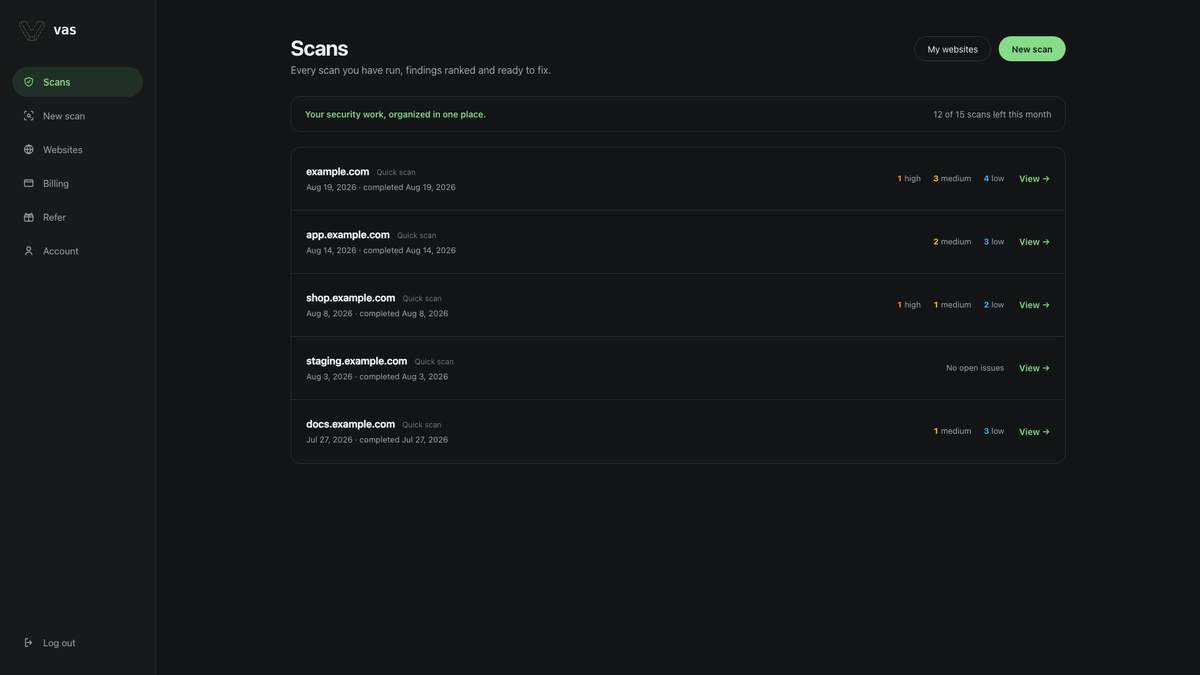
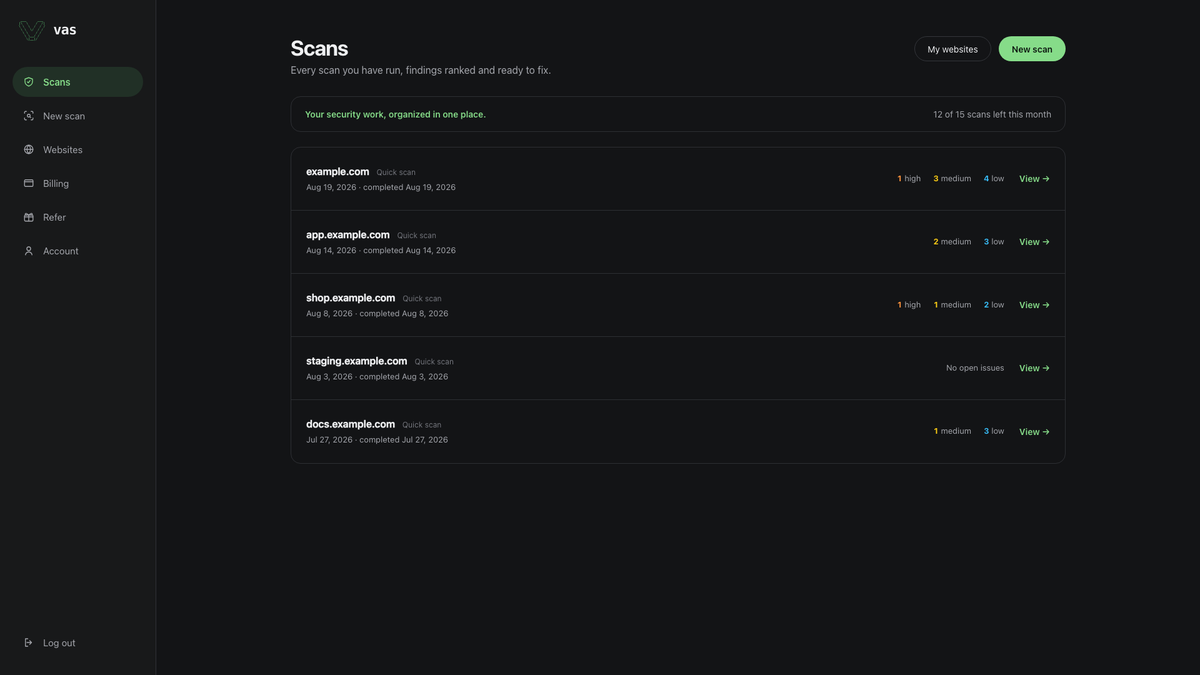
Scan history dashboard
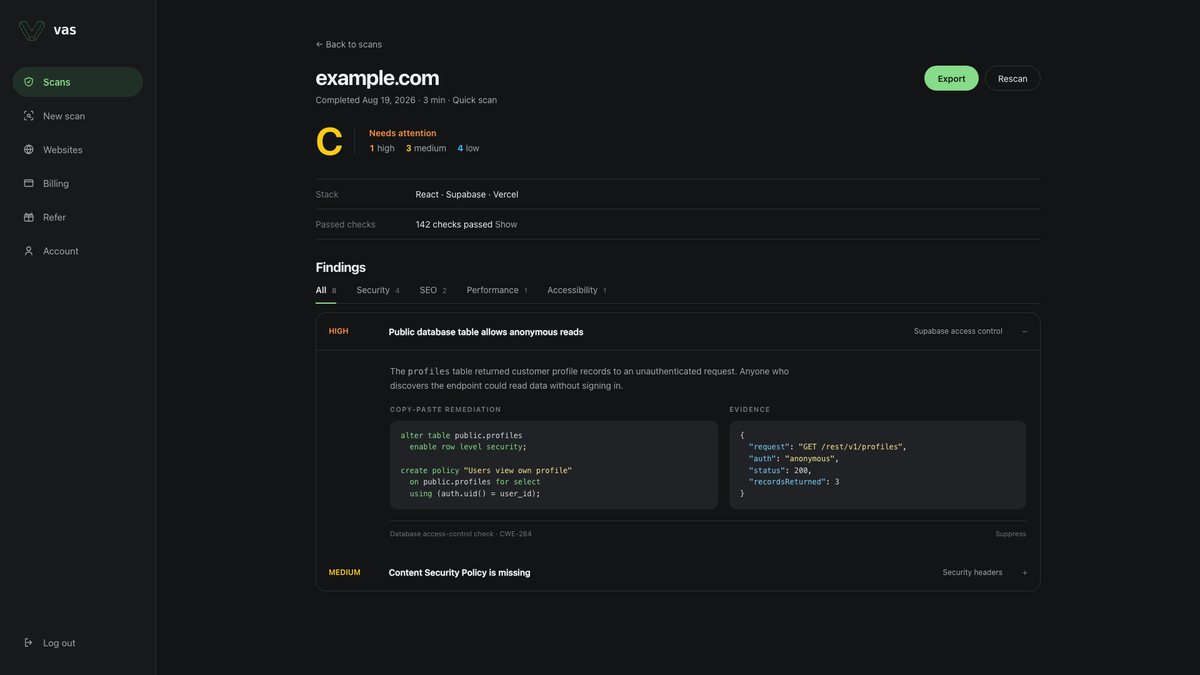
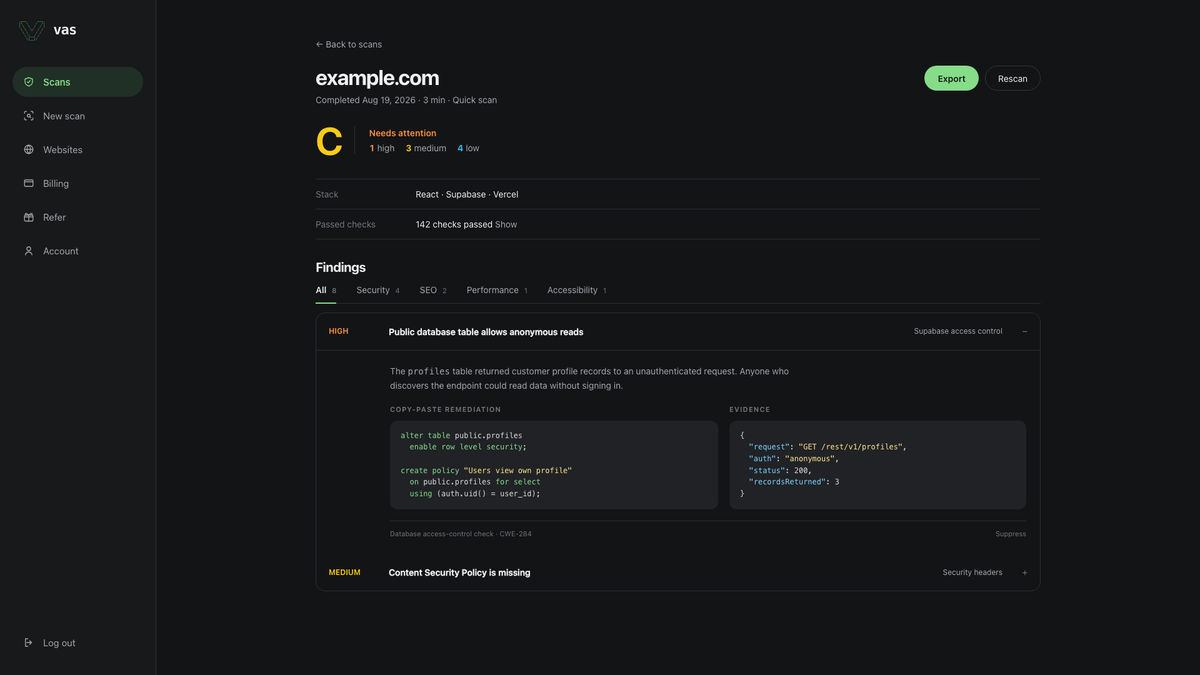
Remediation code and evidence view

Vibe App Scanner

-80%$49
$240
  • Lifetime access
  • Refundable up to 60 days
  • Plus members are covered by our We Got Your Back guarantee
AppSumo Launchpad

Chosen by AppSumo for their potential and innovation

Your AI coding tool can build an app in a weekend, but stress-testing the auth flow is on you. Vibe App Scanner scans your live app the way an attacker would—and hands you the exact fix for every issue.

TL;DR

  • checkmarkDetect exposed API keys, broken auth, and missing RLS before an attacker finds them first
  • checkmarkFix every finding with copy-paste remediation code your AI tool can apply in seconds

Integrations

Google Firebase, Stripe, Supabase

Best for

Developers, Solopreneurs, Agencies

Vibe App Scanner logo

Vibe App Scanner

Rapidly scan and remediate vulnerabilities to secure your app

Scan any app in minutes

  • Enter a URL and let VAS auto-detect your stack—React, Supabase, Vercel, and 20+ platforms recognized out of the box
  • Run 150+ targeted checks tuned for the vulnerabilities AI coding tools most commonly introduce, so nothing slips past
  • Add optional login credentials to test authenticated user flows and catch access-control issues that only appear once signed in
Scan any app in minutes

See every risk, ranked by severity

  • Rank every finding by severity so you fix what would actually get you breached first—not wade through low-priority noise
  • See exactly what was caught with labels, like exposed secrets, RLS misconfigs, and missing headers
  • Get a plain-English explanation of why each issue is dangerous and what an attacker could do with it—not just a CVE number
See every risk, ranked by severity

Monitor your security progress over time

  • Track every scan you've run and watch your security score improve as you work through findings
  • Compare findings across deploys or environments to catch new vulnerabilities the moment they appear, before your users do
Monitor your security progress over time

Apply fixes backed by real evidence

  • Paste ready-to-use remediation code straight into your AI tool or editor and fix the issue without any guesswork
  • Review the raw JSON evidence behind every finding so you can see exactly what VAS tested and why it flagged it
Apply fixes backed by real evidence

Choose the plan that’s right for you

Feel secure in your purchase with AppSumo's 60 day money-back guarantee.

Recommended badgeRecommended
Refundable up to 60 days
Plus members are covered by our
We Got Your Back guarantee
Deal terms & conditions
Vibe App Scanner Licensing V2 (September 2026)
See Vibe App Scanner Licensing V2 (September 2026)
Founded November 21, 2025
🇨🇦Ontario, Canada
1-10
Startup
Bootstrapped

Vibe coding changed how we build. Security needs to catch up.

Hey Sumo-lings 👋

We’re the two founders behind Vibe App Scanner, and between us we’ve spent almost two decades working in cybersecurity.

Before VAS, we were doing code and security audits through our agency. More and more of the apps landing in front of us were built with tools like Lovable, Base44, Replit, Claude, Codex, etc.

A lot of them looked great. They worked. They were ready to show customers.

Then we looked under the hood.

We kept finding the same problems: Supabase tables anyone could read, service-role keys sitting in frontend code, APIs that trusted whatever user ID they were given, and authentication that stopped at “is this person logged in?” without checking what they should actually be allowed to access.

The founders building these apps weren’t careless. The tools had helped them ship quickly, but checking the security still required knowledge most founders understandably don’t have.

We built Vibe App Scanner to make that part much easier.

Paste in the URL of your live app, and VAS checks what is actually exposed. It goes beyond the usual security header checklist to inspect your JavaScript, discover APIs, test database access controls, check authentication, and look for the mistakes we saw during real audits.

It also understands the stacks AI-built apps commonly use. For example, a Supabase anon key is meant to be public. A Supabase service-role key absolutely is not. That distinction sounds simple, but plenty of generic scanners get it wrong.

The bit we’re proudest of is what happens after VAS finds something.

You don’t just get a scary vulnerability name and a link to a technical article. You get the evidence, an explanation you can understand, and a copy-paste fix you can hand straight to Lovable, Cursor, Claude Code or your developer.

Fix it, scan again and check that it’s really gone.

VAS also checks performance, accessibility, SEO, compliance, email security and AI search visibility, so you get a much better idea of whether your app is ready to launch, not just whether the homepage looks finished.

We’re bringing VAS to AppSumo because we know how much this community builds and ships. We also know that most small teams don’t have a security engineer sitting beside them every time they push an update.

We’ll be here throughout the campaign to answer questions, dig into feedback, and improve the checks. If VAS flags something you don’t understand, ask us. If there’s a platform or security check you want us to add, tell us.

We’ve spent years finding the holes. Now we want to help you catch them before someone else does.

Jacob (Co-founder of Vibe App Scanner)

Questions & reviews